APAC CIOOutlook
About UsConferencePartner With Us
  • Technologies
    • Blockchain
      Data Intelligence and Management
      Digital Transformation
      FinTech
      Generative and Agentic AI
      Low Code No Code
      Mobile Application
      Networking
      Robotics
      Storage
      Wireless
  • Industries
    • Automotive
      Aviation
      Banking
      Construction
      E-Commerce
      Food and Beverages
      Healthcare
      Insurance
      Logistics
      Manufacturing
      Retail
      Supply Chain
      Travel and Hospitality
  • Platforms
    • Microsoft
      Salesforce
      SAP
  • Strategic Solutions
    • Business Intelligence
      Contact Center
      Corporate Finance
      CRM
      Cyber Security
      Data Center
      Enterprise Asset Management
      Enterprise Performance Management
      IT Infrastructure and Services
      Managed Services
      Procurement
      Unified Communication
      Workflow
  • Home
  • CXO Insights
  • Leadership Perspectives
  • Innovation Insights
  • Research
  • News
  • Whitepapers
  • CXO Awards
#

Apac CIOOutlook Weekly Brief

×

Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Apac CIOOutlook

Subscribe

loading

THANK YOU FOR SUBSCRIBING

Group IB has been recognized by APAC CIOOutlook Magazine as the recipient of “Top Cyber Security Companies,” based on our proprietary methodology, reflecting its position in the industry. This profile has been developed by the APAC CIOOutlook research and editorial team based on insights from an interview with Sergei Nikitin, COO.

Group IB
The High-fidelity Adversary-Centric Threat Hunting and Intelligence Leaders

Group IB

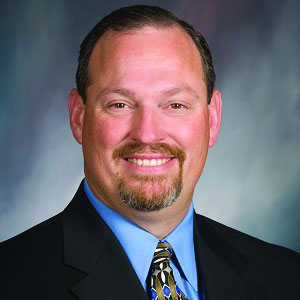
,Sergei Nikitin, COO, Group IB Sergei Nikitin, COO
With the number of online assets that need protection increasing all the time and threat actors exploring new ways to attack their targets, it has become a challenge to ensure cybersecurity. Organizations are constantly plagued with cyberattacks such as DNS tunneling, zero-day exploits, and, most notably, ransomware. While earlier the discussion has been mainly about the little cybersecurity awareness, now the main issue is about understanding what threats and risks target specific geography, industry, or organization.

Investigating cybersecurity incidents worldwide, Group-IB has repeatedly come across cyberattacks on companies that employed solutions of multiple cybersecurity vendors but, nevertheless, fell victim to cybercriminals.

Group-IB has been developing solutions that are built around the attackers. Having conducted over 1,200 investigations worldwide, the company’s analysts acquired an in-depth knowledge of how cybercriminals act, what tactics and instruments they use, and, most importantly, what hazards are relevant to a specific geography, industry, or company. This expertise was gained because of a distributed network of Threat Intelligence & Research Centers worldwide. “Over the past couple of years, we have created outposts in the Asia-Pacific, Europe, and the Middle East that serve as threat intelligence and threat hunting centers supporting the company’s activities,” says Sergei Nikitin, the COO of Group-IB Global HQ in Singapore. “These centers recreate the organizational structure of the company, including all the key service and product divisions Group-IB has and are made up of experts with long-standing experience in investigating sophisticated digital crimes and top local talents who have a deep grasp of cyber threat environment relevant to particular geographies.” This enables Group-IB’s analysts to record cybercrime outbreaks in various parts of the world and, through the prompt data sharing, play an offensive line in containing the distribution of such threats and protecting the company’s customers.

Over the past couple of years, Group- IB has created outposts in the Asia-Pacific, Europe, and the Middle East that serve as threat intelligence and threat hunting centers supporting the company’s activities

Group-IB Threat Intelligence & Attribution (TI&A) is one of the company’s most heavily loaded systems that offers organization-tailored data on threats and adversaries, with the company’s proprietary technologies at its core. Group-IB TI&A enables corporate security teams to analyze threat actors and their TTP to proactively hunt for cybercriminals and shield their network infrastructure against possible attacks. The solution has some special features like threat actor profiling, botnet & phishing data exfiltration, and a unique tool for graph network analysis.

The system also has outstanding human intelligence that stands for the info collected by Group-IB analysts on underground forums and in the dark web, in the battleground incident response or digital forensics activities, as well as part of joint operations with international law enforcement agencies throughout its nearly two-decade history. “Our system gives organizations an overview of attackers targeting it, its partners, and industry, as well as an individual threat landscape. This enables the company to get a fuller picture of online risks it is facing or can face in the future, which cannot be achieved with the help of traditional cybersecurity solutions,” mentions Mr. Nikitin. Further, to mitigate the ransomware problem, which for many organizations starts from phishing emails, the company offers Group-IB Atmosphere, which is an intel-driven cloud malware detonation platform that understands how attackers circumvent traditional sandboxes. It analyzes texts, URLs, attachments, and encrypted objects and surpasses most modern evasion methods.

The focus on adversaries is Group- IB’s major competitive advantage that enables the company not only to assist businesses in probing into cybersecurity incidents that already took place but also in preventing future attacks by promptly detecting the elements of infrastructure created by threat actors for their future attacks. Group-IB has been gathering these traces for the past 18 years, which enabled it to compile profiles of over 100,000 threat actors, with their records being updated on a regular basis. These profiles include IOCs, files, malware samples, tools, and tactics that are mapped to MITRE ATT&CK matrix, along with info on attackers’ potential partners and clients.

In the next couple of years, Group-IB will continue expanding its distributed international network of autonomous cybersecurity centers. This will help the company further intensify its strong knowledge of cyber threats worldwide, polishing up its human intelligence, which is one of the pillars of its TI&A system. “Our geographical expansion will help companies worldwide have a facilitated access to innovative product portfolio. Another work-stream relating to this goal is the development of Group-IB’s MSSP and MDR program that aims to make our solutions and services more accessible to customers all over the world,” concludes Mr. Nikitin..
Share this Article:
Tweet
Share

Company
Group IB

Headquarters
Singapore, SG

Management
Sergei Nikitin, COO,

Description
Group-IB has been developing solutions that are built around the attackers. Having conducted over 1,200 investigations worldwide, the company’s analysts acquired an in-depth knowledge of how cybercriminals act, what tactics and instruments they use, and, most importantly, what hazards are relevant to a specific geography, industry, or company. This expertise was gained because of a distributed network of Threat Intelligence & Research Centers worldwide. Group-IB Threat Intelligence & Attribution (TI&A) is one of the company’s most heavily loaded systems that offers organization-tailored data on threats and adversaries, with the company’s proprietary technologies at its core. Group-IB TI&A enables corporate security teams to analyze threat actors and their TTP to proactively hunt for cybercriminals and shield their network infrastructure against possible attacks

2021

I agree We use cookies on this website to enhance your user experience. By clicking any link on this page you are giving your consent for us to set cookies. More info

CIO Speaks

Previous Next
Cloud Computing: Pharma Takes the Plunge

Andy Newsom, SVP & CIO, CSL Behring

WiFi 6, 5G and the Internet of Things (IoT)

Mark Badal, CIO, IT&E

In Augmented Reality, Size Matters

Jason Blackman, CIO, Carsales.Com

Enhancing Customers

Marc A. Hamer, VP & CIO, Babcock & Wilcox Enterprises, Inc.

Cloud or On-Premise? When Would The Question End?

Kevin Soh, CIO and Director, e-Strategies, BH Global Corporation

Responsible AI: The Human-Machine Symbiosis

Sal Cucchiara, CIO & Head Of Wealth Management Technology, Morgan Stanley

Diversity and Inclusion can Drive Better Solutions for Clients and Employee Engagement

Linda K. Lannen, CIO & Sr. VP, Kleinfelder

Cyber Security - Integrated enterprise approach required to address the multifaceted challenges

Sumit Puri, CIO, Max Healthcare

The Great Tech Arms Race: How Changing Consumer Behaviour and Expectation is Driving Ecommerce Transformation

Brett Raven, CIO, Big Red Group

Relying On Technologies To Transform Data Into Information

Mark Ohlund, CIO & Sr. V.P., Armada Supply Chain Solution

3D Printing Requires Wildly Different Thinking

James MacLennan, SVP & CIO, IDEX Corporation

Achieving Service Excellence Through The Digital Utility

Thomas Kuczynski, CIO, DC Water

APAC CIOOutlook
Follow on LinkedIn

About

  • Home
  • About Us
  • Partner With Us

Stay Connected

  • Subscribe
  • Newsletter
  • Sitemap

Contact Us

  • editor@apacciooutlook.com
  • sales@apacciooutlook.com
  • marketing@apacciooutlook.com

Legal

  • Editorial Policy
  • Privacy Policy
  • Terms of Use

© 2026 APAC CIOOutlook. All rights reserved. Headquarteblue in Fort Lauderdale, FL, USA.

This content is copyright protected

However, if you would like to share the information in this article, you may use the link below:

https://www.apacciooutlook.com/group-ib